Network Sniffing Techniques: A Comprehensive Review Paper
Krishnesh Singh, Roll no. 38
MSc.IT (Part II) student
Patkar Varde College, Goregaon
Abstract:
Network communication forms the backbone of modern computing environments, facilitating the exchange of information across various devices and systems. However, this constant flow of data also introduces security challenges, as malicious actors seek to intercept sensitive information. Network sniffing, the process of capturing and analyzing network traffic, has been both a valuable tool for network administrators and a vector of attack for cybercriminals. This research paper provides an in-depth review of network sniffing techniques, including their classification, tools, countermeasures, and ethical considerations. By understanding these techniques, network administrators can better defend against potential attacks, and researchers can continue to develop effective countermeasures.
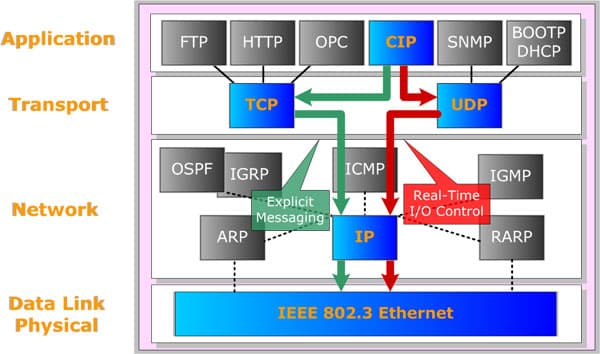
The proliferation of interconnected devices and the ubiquity of the internet have transformed the way we communicate and conduct business. However, the exchange of data across networks also opens the door to potential security breaches. Network sniffing, also known as packet sniffing or packet analysis, is the process of intercepting and inspecting data packets as they traverse a network. While it is an essential tool for diagnosing network issues and optimizing performance, it can also be exploited by malicious actors to gather sensitive information.
Network sniffing techniques can be broadly classified into two categories: passive and active. Passive techniques involve monitoring network traffic without altering it, while active techniques require generating additional traffic to manipulate the network's behavior.
2.1 Passive Sniffing Techniques:
Hub-Based Sniffing:
Hub-based sniffing involves connecting the monitoring device to a network hub, where all traffic is replicated to each port. This allows the device to capture all data passing through the hub.
Switch Port Mirroring:
In switched networks, port mirroring is used to duplicate traffic from one or more switch ports to a monitoring port. This technique allows administrators to capture traffic for analysis.
2.2 Active Sniffing Techniques:
ARP Poisoning/ARP Spoofing:
Address Resolution Protocol (ARP) poisoning involves sending falsified ARP messages to redirect traffic to the attacker's device, enabling them to intercept and analyze the data.
DNS Spoofing:
Domain Name System (DNS) spoofing manipulates DNS responses to redirect network traffic to the attacker's server, allowing them to capture sensitive information.
Numerous tools are available for network sniffing, catering to various needs and skill levels. Notable tools include Wireshark, tcpdump, Snort, Ettercap, and Cain and Abel. These tools provide functionalities for capturing, analyzing, and visualizing network traffic.
Wireshark is one of the most popular and powerful open-source packets sniffing tools. It allows users to capture, analyze, and visualize network traffic in real-time. Wireshark supports various protocols and provides detailed packet-level information.
tcpdump is a command-line packet analyzer that runs on Unix-like operating systems. It captures network packets and displays them in a human-readable format. tcpdump is widely used for network troubleshooting and monitoring.
Snort is an open-source intrusion detection and prevention system that can also be used for packet sniffing. It analyzes network traffic in real-time, detects malicious patterns, and alerts administrators about potential threats.
These tools cater to different needs and levels of expertise, from basic packet capture to advanced intrusion detection and analysis. It's important to use these tools responsibly and ethically, ensuring that they are used for legitimate purposes such as network troubleshooting, security assessments, and research.
To mitigate the risks associated with network sniffing, several countermeasures can be implemented:
- Encryption: Encrypting data before transmission ensures that even if intercepted, the data remains unreadable.
- Network Segmentation: Dividing networks into segments with controlled access limits the potential scope of network sniffing attacks.
- Intrusion Detection/Prevention Systems (IDS/IPS): These systems monitor network traffic for suspicious activities and can take automated actions to prevent attacks.
- Port Security: Implementing port security features on switches can prevent unauthorized devices from accessing the network.
While network sniffing is a valuable tool for maintaining network integrity, its misuse raises ethical concerns. Unauthorized sniffing of personal or confidential data can lead to privacy violations and legal consequences.
Network sniffing techniques play a dual role in modern networking environments. They offer valuable insights for network administrators while also posing potential threats if misused. Understanding the classification, tools, countermeasures, and ethical implications of network sniffing is crucial for creating robust network security measures that protect against unauthorized data interception.
https://learn.microsoft.com/en-us/archive/blogs/
https://en.wikipedia.org/wiki/International_Computer_Security_Association
https://www.zdnet.com/home-and-office/networking/the-six-dumbest-ways-to-secure-a-wireless-lan/
https://www.wi-fiplanet.com/understanding-802-11-frame-types/