What is penetration testing?
A penetration test (also known as pen test) is an authorized simulated attack performed on a computer system to evaluate its security. Pen-testers use the same tools, techniques, and processes as attackers to find and demonstrate the business impacts of weaknesses in a system. Penetration tests usually simulate a variety of attacks that could threaten a system. They can examine whether a system is robust enough to withstand attacks from an unauthenticated position.
Why is penetration testing needed?
Pen tests provide detailed information on actual, exploitable security threats. By performing a penetration test, you can identify which vulnerabilities are most critical, which are less significant, and which are false positives.
Organizations use penetration testing for large and complex business-critical operations, as well as for custom components. Pentesting is necessary when developing software that handles sensitive data, such as financial assets, customer information and transaction data. Sensitive sectors—including government, medical and financial services industries—are highly regulated and thus require strong security measures.
If your organization has been infiltrated, you can leverage pentesting to help identify the weaknesses that enabled the breach and learn how to remediate them. You can also detect other vulnerabilities, which may not have been exploited, to prevent further attacks in the future.
How is penetration testing carried out?
We will now dive into how it is carried out, the steps and the processes involved during penetration testing.
1.Plan – start by defining the aim and scope of a test. To better understand the target, you should collect intelligence about how it functions and any possible weaknesses.
2. Scan – use static or dynamic analysis to scan the network. This informs pentesters how the application responds to various threats.
3. Gain access – locate vulnerabilities in the target application using pentesting strategies such as cross-site scripting and SQL injection.
4. Maintain access – check the ability of a cybercriminal to maintain a persistent presence through an exploited vulnerability or to gain deeper access.
5. Analyze – assess the outcome of the penetration test with a report detailing the exploited vulnerabilities, the sensitive data accessed, and how long it took the system to respond to the pentester’s infiltration.
With all the steps involved, it is never the same for every test as the tests themselves differ in types; following are the types of penetration testing:
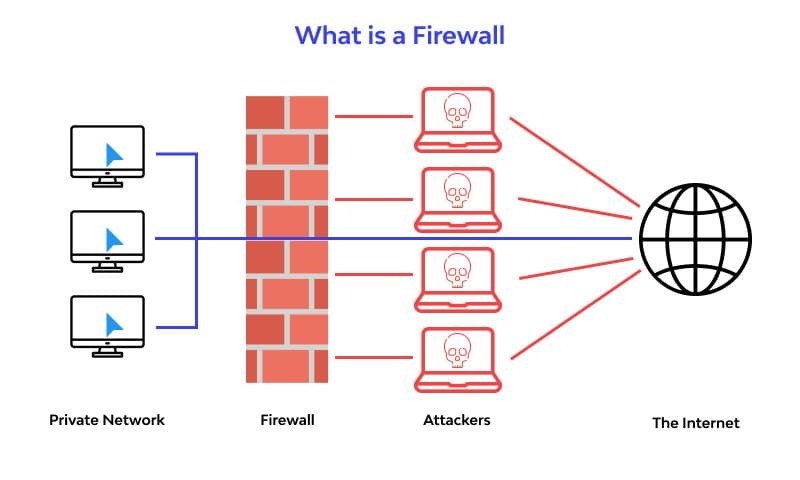
A] Network Services Penetration Testing – The term network services testing, also known as infrastructure testing, refers to a type of pentest performed for the purpose of protecting the organization from common network attacks.A network services pentest typically checks various components of the infrastructure, including servers and firewalls, switches and routers, workstations and printers. The goal of a network services pentest is to discover the most exposed security weaknesses and vulnerabilities in the network—before attackers can exploit these blindspots.
B] Web Application Penetration Testing – The purpose of a web application pentest is to identify security weaknesses or vulnerabilities in web applications and their components, including the source code, the database, and any relevant backend network.
A web application penetration testing process typically performs the following three phases:
C] Social Engineering Penetration testing – A social engineering attack targets employees of the company or parties with access to company assets, trying to persuade, trick, or blackmail them into disclosing information and credentials. A social engineering pentest tries to determine how the organization copes during a social engineering attack.
These were some of the types of test, now we will move on to tools for penetration testing.
Getting better actionable results on pen testing is greatly dependent on the types of tools being used.Typically, a pentest leverages several types of tools to ensure visibility into a greater scope of vulnerabilities and weaknesses. There is no one-size-fits-all tool for pen testing. Instead, different targets require different sets of tools for port scanning, application scanning, Wi-Fi break-ins, or direct penetration of the network. Broadly speaking, the types of pen testing tools fit into five categories.